Best Practices for Keeping Software and Devices Updated
In today’s interconnected digital environment, keeping software and devices updated is a fundamental aspect of maintaining a secure and reliable system. Updates often include patches for security vulnerabilities, improvements to functionality, and fixes for bugs that could otherwise be exploited. The process of updating involves not only installing the latest versions but also ensuring that these updates are applied consistently across all devices and applications. Without a structured approach, it is easy for critical updates to be overlooked, leaving potential gaps in security. This article explores best practices for managing updates, with a focus on automation and verification methods that can help streamline the process.
Many organizations and individuals recognize the importance of updates, but the sheer volume of devices and software can make manual updating impractical. Automation tools can assist in deploying updates efficiently, but they require careful configuration and monitoring. Similarly, verifying that updates have been successfully installed is essential to confirm that protections are in place. By adopting a systematic approach, it is possible to reduce the risk of unpatched vulnerabilities and maintain a more consistent security posture. The following sections outline key considerations and steps for effective update management.
It is important to note that while updates are a critical component of security, they are not a standalone solution. The effectiveness of updates depends on various factors, including the specific environment, user behavior, and the presence of other security measures. Therefore, the practices described here should be adapted to fit the unique needs and constraints of each situation. The goal is to provide a framework that can be tailored to different contexts, rather than a one-size-fits-all solution.
Understanding the Importance of Regular Updates
Regular updates are a primary defense against known security vulnerabilities. Software vendors frequently release patches to address flaws that could be exploited by malicious actors. When these patches are not applied, devices and applications remain vulnerable to attacks that could compromise data, disrupt operations, or lead to financial loss. The window between the disclosure of a vulnerability and the availability of an exploit can be short, making timely updates crucial. However, the mere availability of an update does not guarantee protection; it must be installed and verified.
Beyond security, updates can also enhance performance, add new features, and improve compatibility with other systems. For example, operating system updates might include driver improvements that resolve hardware issues, while application updates might introduce new functionalities that increase productivity. These benefits, however, are contingent on updates being applied correctly. In some cases, updates can introduce new problems, such as compatibility issues or unexpected behavior, which is why testing and verification are important steps in the update process.
The frequency of updates varies depending on the software and the vendor’s release cycle. Some applications receive updates weekly, while others may only be updated quarterly or annually. Keeping track of these schedules manually is challenging, especially in environments with many devices. This is where automation can play a significant role, helping to ensure that updates are not missed and that they are deployed in a consistent manner.
Developing an Update Management Strategy
An effective update management strategy begins with an inventory of all software and devices within the environment. This inventory should include details such as the operating system, application versions, and the criticality of each system. Understanding what needs to be updated and how often is the foundation for any automation or verification process. Without a clear inventory, it is difficult to ensure that all components are covered.
Once the inventory is established, the next step is to define policies for update deployment. These policies should specify how updates are approved, scheduled, and installed. For example, some organizations may choose to test updates on a small group of devices before rolling them out broadly. Others may rely on vendor-recommended settings or automatic updates. The policy should also address how to handle updates that require reboots or that may disrupt user activities. Clear policies help reduce confusion and ensure that updates are applied consistently.
Another consideration is the use of centralized management tools. These tools can automate the deployment of updates across multiple devices, often providing reporting features that show which devices have been updated and which have not. Many enterprise environments use solutions like Microsoft Endpoint Configuration Manager, Jamf, or similar platforms. For individuals, built-in update mechanisms in operating systems and applications can be sufficient, but they still require some configuration to ensure they are enabled and functioning as intended.
Automating Update Deployment
Automation can significantly reduce the manual effort required to keep software and devices updated. By configuring systems to automatically download and install updates, organizations can ensure that patches are applied promptly without relying on individual users to take action. However, automation is not without its challenges. It requires careful planning to avoid unintended consequences, such as updates that break critical applications or that consume excessive bandwidth during peak hours.
To automate updates effectively, consider the following steps:
- Enable automatic updates where available, such as in operating systems, web browsers, and productivity software.
- Use a centralized management tool to schedule and deploy updates across multiple devices, with options to control the timing and scope of deployments.
- Configure update settings to download and install updates during off-hours to minimize disruption.
- Set up notifications or alerts to inform administrators of pending updates or failed installations.
- Regularly review and adjust automation settings to align with changing needs and vendor recommendations.
It is important to test automated updates in a controlled environment before widespread deployment. This can help identify potential issues and allow for adjustments to be made. Additionally, maintaining a rollback plan in case an update causes problems is a prudent practice. Automation should be seen as a tool that supports, but does not replace, human oversight.
Verifying Update Installation
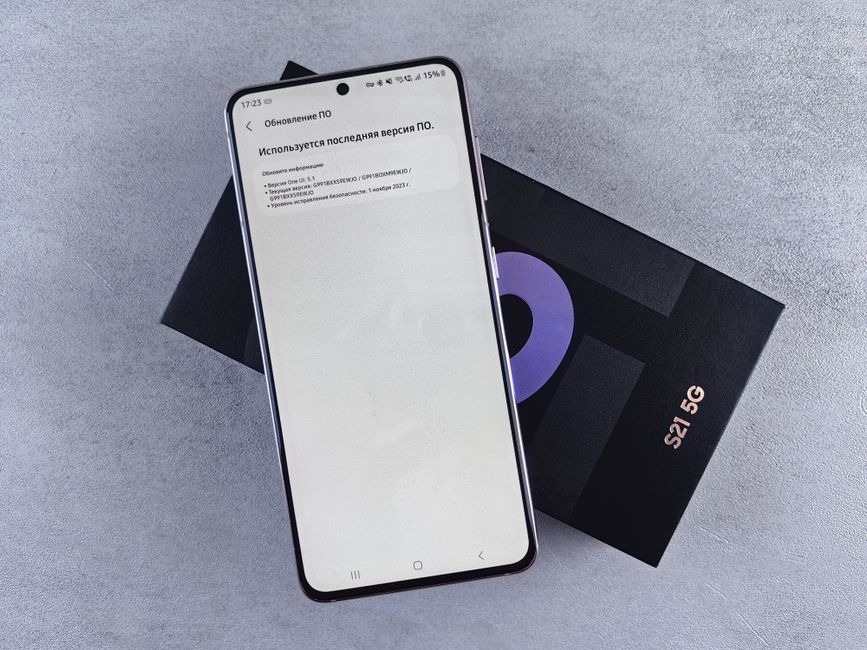
Verification is a critical step that is often overlooked. Even with automation, there is no guarantee that updates have been successfully installed on every device. Factors such as network issues, insufficient storage, or user interference can cause updates to fail. Therefore, it is essential to have mechanisms in place to verify that updates have been applied and that devices are running the expected versions.
Verification can be performed through several methods:
- Manual checks: Periodically review device settings or use system information tools to confirm update status.
- Automated reporting: Leverage management tools that provide dashboards or reports showing update compliance across the fleet.
- Vulnerability scanning: Use scanning tools to identify missing patches and prioritize remediation efforts.
- Log analysis: Examine update logs to detect errors or failures that may require attention.
In addition to these methods, it is beneficial to establish a baseline of expected versions and configurations. Any deviation from this baseline can trigger an alert for further investigation. Verification should be an ongoing process, not a one-time event, as new updates are released regularly. By integrating verification into the update cycle, organizations can gain confidence that their defenses are up to date.
Regular verification helps ensure that updates are not only deployed but also effective in addressing the vulnerabilities they are intended to fix.
Addressing Common Challenges and Best Practices
Despite the benefits of automation and verification, several challenges can arise. One common issue is update fatigue, where users and administrators become overwhelmed by the frequency of updates and may delay or ignore them. To mitigate this, it is helpful to prioritize updates based on risk, focusing first on critical security patches. Another challenge is compatibility, as updates can sometimes conflict with existing software or hardware. Thorough testing and phased rollouts can help reduce these risks.
Best practices for update management include maintaining accurate documentation of all software and devices, establishing clear policies and responsibilities, and leveraging automation where feasible. It is also important to stay informed about vendor advisories and security bulletins to understand the urgency of updates. For organizations with limited resources, considering a managed service provider or using cloud-based management tools can help bridge gaps in expertise. Ultimately, the goal is to create a repeatable process that can adapt to changing circumstances.
In conclusion, keeping software and devices updated is a continuous effort that requires planning, automation, and verification. By following the practices outlined in this article, individuals and organizations can improve their ability to manage updates efficiently. While no approach can guarantee absolute security, a systematic and informed strategy can significantly reduce the likelihood of unpatched vulnerabilities being exploited. It is advisable to review and refine update processes regularly to ensure they remain effective and aligned with evolving threats.